
CISO Perspective Agent Identity / SERVICE_AGENT Cortex AI Gateway Preview Updated 17 Sep 2026 Insights · AI Security and Identity AI agents are becoming privileged identities Snowflake’s work on...
Under 32 CFR § 170.22, the Affirming Official is defined by responsibility and authority, not by title. A CISO may qualify. So may an owner. A systems administrator who knows the environment best...
CMMC Regulatory Brief · 01 Class Deviation 2026-O0025 Rev. 3 DFARS Part 240 · FAR Part 40 Updated 09 Sep 2026 Insights · CMMC & NIST SP 800-171 C3PAO wasn’t removed. Read the status list...
AI Governance Brief · 02 DFARS 252.204-7012 · NIST SP 800-171 · FedRAMP CUI & Generative AI Updated 06 Sep 2026 Insights · AI Governance Can you put CUI into generative AI? The honest answer is...
Vendor Brief · 01 32 CFR 170 · DFARS 252.204-7012 · NIST SP 800-171 ESP / SPA Scoping Updated 06 Sep 2026 Insights · AI Governance Are AI vendors ESPs or SPAs under CMMC? The question assumes the two...
what the Phase 2 pause did not change Two separate obligations that contractors routinely collapse into one. The certification milestone is suspended; the self-assessment, the posted score and the...
Innovation Without Control Is Risk An engineer pastes a firewall config into a chat window and solves the problem in four minutes. Why that is a control failure, and how to permit AI use without...
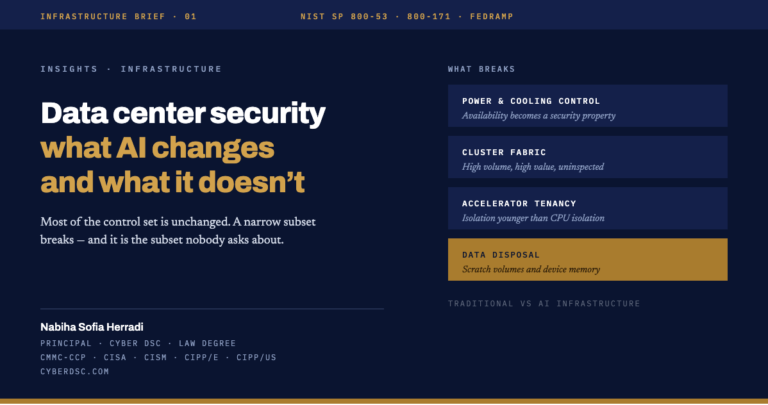
What AI changes, and what it doesn’t Four areas where AI workloads genuinely alter the control set — power and cooling, cluster fabric, accelerator tenancy, data disposal — and the much longer list...
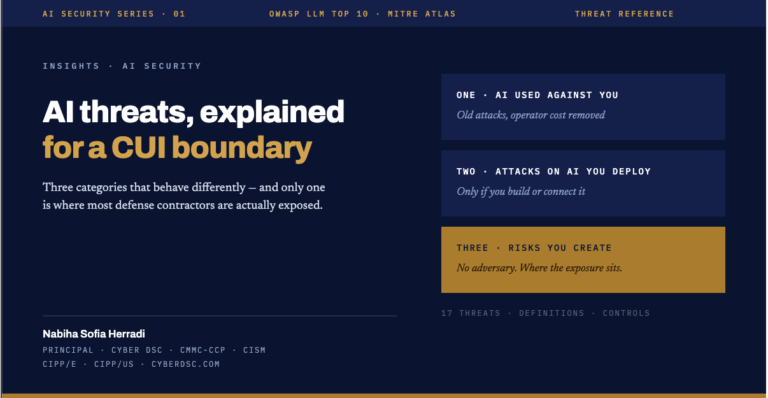
defined for a CUI environment Most threat lists mix three unrelated things: AI used against you, attacks on the AI you deploy, and risk you create yourself. Separating them is what makes the list...
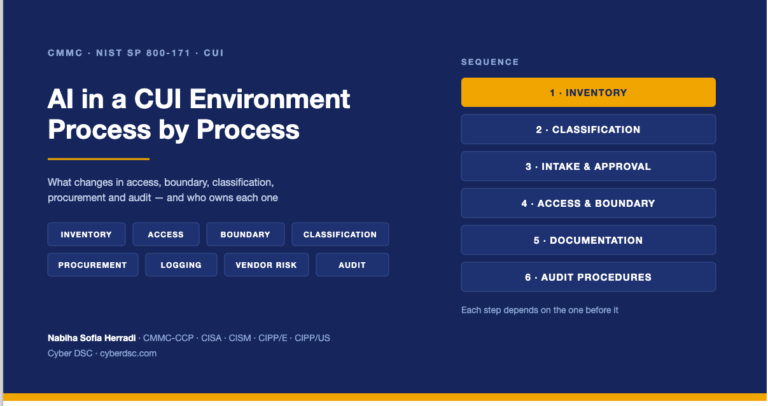
What Actually Changes in Each Governance Process This is not a new compliance program. Walking through inventory, access management, boundary control and classification to show which existing...
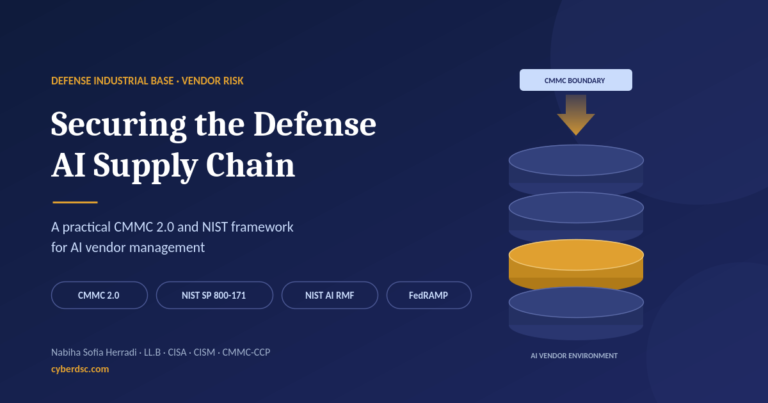
A Practical CMMC 2.0 and NIST Framework for Vendor Management Your vendors are shipping AI features you did not evaluate. A working approach to assessing AI in the supply chain against CMMC and NIST...
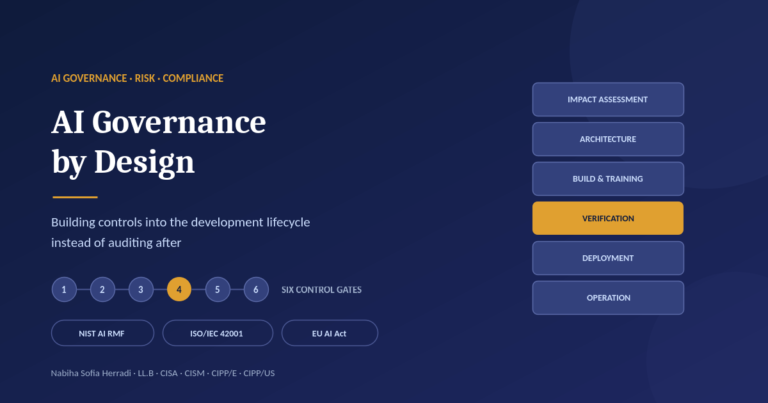
Building Controls Into the Development Lifecycle Most AI governance programs are assembled in the wrong order — after the model is in production, when someone asks what it was trained on. What it...